


Bank-Grade Compliance,
Certified Trust
& Enterprise Security
Security, regulatory rigor, and zero-trust data protection are foundational to every API packet and message we route. Explore Alot Solutions' globally accredited ISO certifications, sovereign Indian data residency, HSM key protection, and independent audits engineered for enterprise scale.
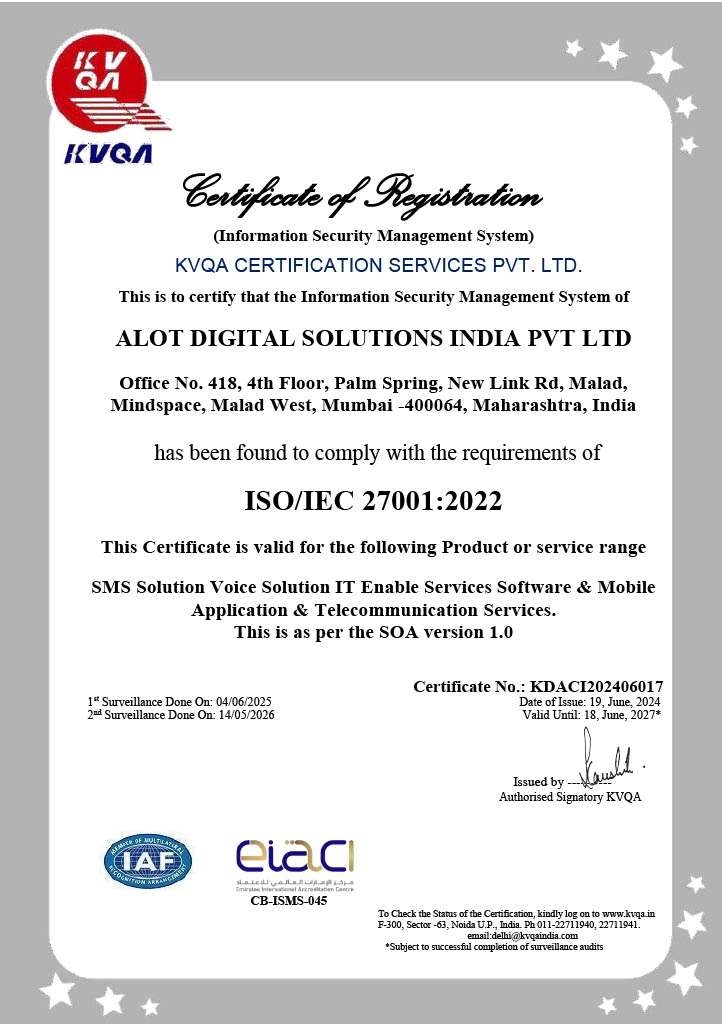
Audited Information Security Management System covering all cloud infrastructure, API gateways, database encryption, access controls, and telecom routing nodes.
Official Certificates & Recognitions
Independently audited by international certification bodies to guarantee end-to-end data integrity, operational resilience, and telecom compliance.
ISO/IEC 27001:2022
Certifies that Alot Solutions operates a rigorously audited Information Security Management System covering all cloud infrastructure, API gateways, database encryption, access controls, and telecom routing nodes.
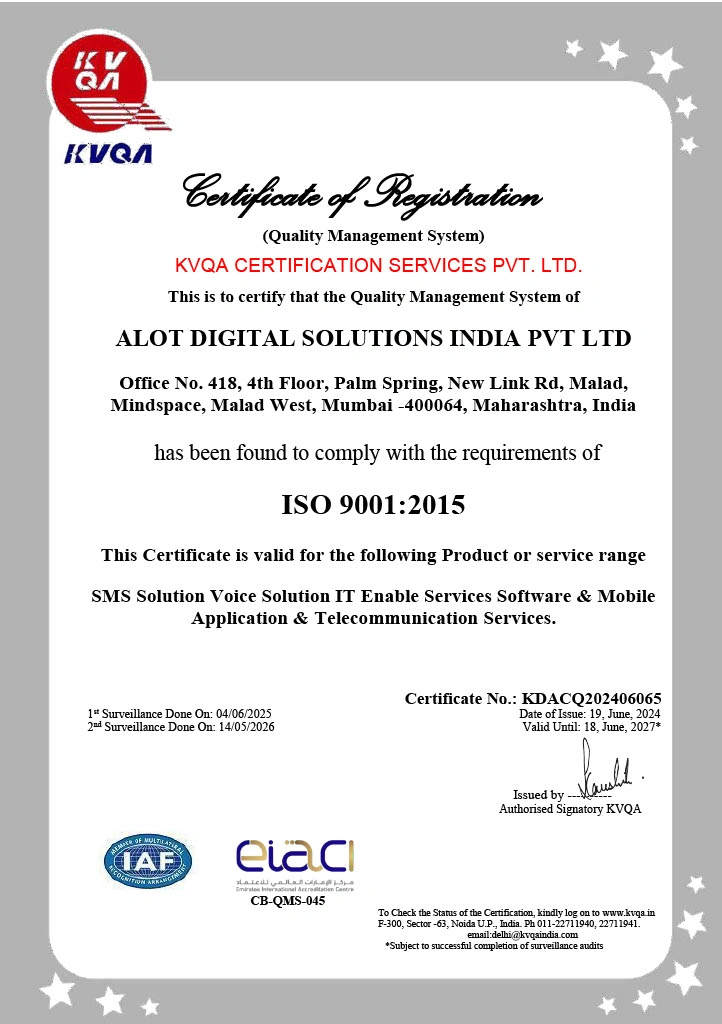
ISO 9001:2015
Validates our organizational processes, customer support responsiveness, systematic risk evaluation, and continuous quality enhancements across all telecommunications messaging products.
Built for Highly-Regulated Banking & Enterprise Sectors
Alot Solutions infrastructure is engineered to adhere to strict telecom and financial sector guidelines including India TRAI DLT registration, RBI two-factor authentication rules, and sovereign data residency.
How We Protect Enterprise Communications
Security and privacy are core to how we operate. We follow best practices across access controls, auditing, monitoring, data handling, and incident response.
Access Controls & Secure Key Management
Granular Role-Based Access Controls (RBAC), multi-factor authentication (MFA) on all consoles, and hardware security module (HSM) based API token management.
- ✓ Enforced MFA & SSO (SAML 2.0)
- ✓ Automated API token expiration
Data Minimization & Retention Controls
Zero plain-text PII storage. All OTPs, customer phone numbers, and transactional payloads are masked or purged based on customer-defined retention schedules.
- ✓ Dynamic PII anonymization
- ✓ Customizable auto-purge rules
Audit Logs & Delivery Traceability
Immutable SIEM activity logs recording every API dispatch, carrier DLR receipt, user login, and administrative action with sub-millisecond precision.
- ✓ Tamper-proof log forwarding
- ✓ End-to-end packet tracking
Vendor & Telco Risk Review
Continuous supplier evaluation covering all telecom carriers, cloud hosting providers, and third-party dependencies with quarterly VAPT exercises.
- ✓ Third-party penetration testing
- ✓ Strict SLA adherence auditing
Incident Response & 24/7 NOC Monitoring
Round-the-clock Security Operations Center (SOC) monitoring with automated threat response, real-time DDoS mitigation, and sub-15 minute P1 SLA escalation.
- ✓ 24/7 Mumbai NOC engineering team
- ✓ Automated carrier failover routing
End-to-End Cryptography & Encryption
State-of-the-art TLS 1.3 protocol for all data in transit across public networks, combined with AES-256 bit encryption for all stored records and databases.
- ✓ TLS 1.3 in transit (PFS)
- ✓ AES-256 data at rest
Compliance & Security FAQ
Answers regarding audit requests, data privacy, and compliance certifications.
Can our enterprise security team review the full ISO 27001 audit report?
Yes. We provide complete ISO 27001 / ISO 9001 certificates and our SOC 2 Type II assessment report to enterprise prospects and clients under standard mutual Non-Disclosure Agreements (NDA).
Where is customer data stored, and is sovereign data residency guaranteed?
All Indian messaging and transactional data resides within certified Tier-3 and Tier-4 data centers in Mumbai, India, in complete alignment with the India Digital Personal Data Protection (DPDP) Act 2023 and RBI guidelines.
How do you handle TRAI DLT header sync and content template scrubbing?
Our platform includes an automated DLT validation engine that binds Principal Entity IDs, verifies sender headers, scrubs variables against registered templates, and checks DND preferences before any SMS is pushed to the carrier SS7 network.
Need a Custom Security or Compliance Assessment?
Our Mumbai security and compliance team is available to complete your vendor security questionnaires, provide VAPT reports, or arrange architecture reviews.